How To Stop Visitors Collecting your Usernames With BetterShield?
Close the places WordPress hands visitors your usernames: the REST API, ?author= links, the users sitemap, embeds, and the sign-in and reset forms.
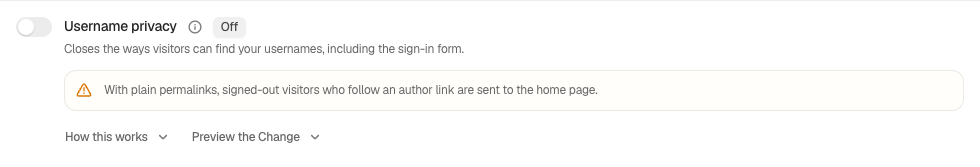
In BetterShield, Username privacy closes the routes a signed-out visitor can use to collect your site’s usernames, the sign-in form included. It is off until you turn it on, under Hide site details on BetterShield › Protection › Hardening. Quick Setup offers the same fix as Stop username discovery.
What it does
It changes seven answers. Five change only for visitors who are not signed in; the users sitemap and an SEO plugin’s author sitemap are withdrawn for everyone. The block editor and the Users screen work as before.
| Where | What WordPress answers by default | With the fix on |
|---|---|---|
| The REST API user list, /wp-json/wp/v2/users | Every account that has published a post, with its slug | 404, as if the route did not exist (one user by number too) |
| ?author= with a number, such as /?author=1 | A redirect to that author’s archive, whose address carries the slug | The visitor is sent to the home page |
| The users sitemap, wp-sitemap-users-1.xml | Every author’s archive | Left out of the sitemap index, and a direct request answers 404. Posts and pages stay. |
| An SEO plugin’s author sitemap, author-sitemap.xml and its pages | Every author’s archive | 404, and the author lists those plugins build into other sitemaps are emptied |
| Embeds of your posts | The author’s name and archive link | Neither |
| The sign-in form | Whether the username exists or the password was wrong | “The username or password you entered is incorrect.” either way |
| The lost-password form | That no account matches | The same “check your email” page a real request reaches |
- Only a numeric ?author= is redirected. An archive at its own address, such as /author/jane/, still works: that address already shows the slug.
- Messages BetterShield shows itself are unchanged, such as a sign-in pause or the puzzle, and the form still shakes for a wrong password.
- On the lost-password form, an empty field still gets its error, and no email goes out for a name or address with no account. In the fix’s own words: “Somebody who mistypes their address is told a link is on its way and no email arrives, which is the trade this makes.”
- It writes no files.
Step 1: Open BetterShield › Protection › Hardening
Open BetterShield › Protection › Hardening and find Username privacy under Hide site details.
Step 2: Stop visitors collecting your usernames
- Press Preview the change. It lists every change above and changes nothing.
- Turn the switch on. The row shows On since and Undo never expires.
It has no options, and Monitor first cannot watch it in advance: its panel points you back to the preview. Other ways to turn it on:
- Findings: Anyone can see your usernames has Apply Fix.
- Quick Setup: Stop username discovery, one of the five safe fixes.
- WP-CLI:
wp bettershield harden user_enumeration --user=adminapplies it;--dry-runpreviews and--undoreverses. See WP-CLI commands. - An AI assistant allowed to make changes can apply it. Taking it off needs a plan you agree to.
If the row names another security plugin that already does this, leave the job to one of them. A note that another plugin already filters the REST API routes is safe to apply over: “nothing breaks, and removing either leaves the other in place.”
Recommended settings
We recommend it on most sites. A username keeps nobody out, but there is no reason to hand out a list of real ones. It matters less than sign-in lockouts and two-factor, so put those in place first.
| Site | What we recommend |
|---|---|
| Membership or course site | On, then open any member or instructor directory while signed out. If it lists people from the public user list, leave the fix off. |
| Agency or many sites | On every site, from Quick Setup or with WP-CLI. On a network, each site has its own switch. |
What it can break, and how to undo
- Author directories that read the public user list. In the finding’s words: “Could break: nothing on most sites. Sites embedding author directories from the public API would need the block removed.” The same goes for a separate front end or app that reads authors without signing in.
- Author links on plain permalinks. Without pretty permalinks, WordPress links each author’s archive as ?author= with a number, so those links take signed-out visitors to the home page.
- A mistyped reset address. The person is told a link is on its way, and none arrives. If someone says their reset email never came, check the address they typed.
- Sitemap and embeds. Author archives leave WordPress’s built-in sitemap and an SEO plugin’s sitemaps (they still exist, and posts still link to them), and a post embedded on another site no longer names its author.
To undo, turn the switch off. Every answer goes back to WordPress’s own at once, and “Hardening undone” is logged. With Ask for my password before removing a protection on, that asks for your password. Safe mode pauses the fix, and deactivating BetterShield stops it.
Final Outcome
Findings. Anyone can see your usernames (Low, in Sign-in & accounts) closes when you apply the fix. It opens again if the switch is on but the fix was not in place on a page a visitor received.
- The row. Within a few visitor page views, a line under the switch says whether everything the fix closes was in place on that page.
- The activity log. “Hardening applied”, and “Finding resolved” for the finding.
- From outside. In a private window, open /wp-json/wp/v2/users (404), /?author=1 (the home page) and /wp-sitemap-users-1.xml (404). Then sign in with a made-up username: you get the same message as a wrong password.
Good to know
Your theme can still link each post to its author’s archive, whose address carries the slug WordPress made from the username. Publishing from an account that cannot manage the site keeps administrator usernames off public pages.
Related
- Hardening
- Stop uploads listings
- Hide sensitive files
- Hide the WordPress version
- Sign-in lockouts
- WordPress user enumeration, explained
This is how you can stop visitors collecting your usernames with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.