How To Send the Four Standard Security Headers With BetterShield?
Add X-Content-Type-Options, X-Frame-Options, Referrer-Policy and Permissions-Policy with one switch, see what each can affect, and undo it.
In BetterShield, Browser protections adds four standard headers that ask the browser to be stricter with your pages. Visitors see no difference. It is under HTTPS and browser security on BetterShield › Protection › Hardening, and it starts off.
What it does
| Header | Value | What it tells the browser |
|---|---|---|
X-Content-Type-Options | nosniff | Use the file type the server declares, never guess. |
X-Frame-Options | SAMEORIGIN | Only your own site may show these pages in a frame. |
Referrer-Policy | strict- | On links to other sites, pass on your domain, not the full address. |
Permissions-Policy | browsing-topics=() | Leave these pages out of the Topics API, used for ad topics. |
- It covers front-end pages, the sign-in page, the REST API and the dashboard. “WordPress sends two of the four to the dashboard itself; this adds the two it does not.”
- A header already present on the response is left untouched.
- Once a day, it asks your site’s own front page which of the four your web server sends on its own, and leaves those to the server from then on. The row then says so, for example: “Your server already sends X-Frame-Options. This item leaves those to it and sends the rest.”
- It does not send HSTS, which “can make a site unreachable and belongs behind its own decision.” See HSTS.
For what each header guards against, see WordPress security headers, explained.
Step 1: Open BetterShield › Protection › Hardening
On BetterShield › Protection › Hardening, find Browser protections under HTTPS and browser security.
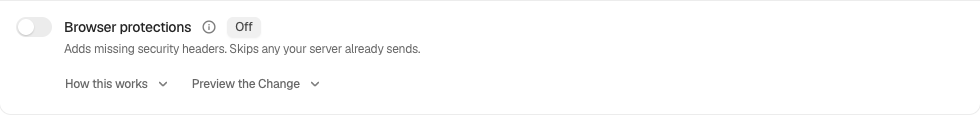
Step 2: Send the four standard security headers
- Press Preview the change. It lists the lines above and changes nothing.
- Turn the switch on. The row shows On since and Undo never expires, then “Confirmed on a page a visitor received” once a visitor’s page has carried the headers.
There are no options. Monitor first has no watch mode for this fix; its panel points you to the preview and the undo.
Other ways to turn it on:
- Quick Setup, under Safe fixes, as Add security headers.
- Apply Fix on the finding Your site doesn’t send some standard browser safety settings, on BetterShield › Findings, which turns it on straight away.
wp bettershield harden security_headers --user=<login>from the terminal, with--dry-runto preview and--undoto turn it off. See WP-CLI commands.- A connected AI assistant allowed to make changes can turn it on directly. Turning it off needs a plan you agree to.
If Patchstack is active and licensed, with its own security headers setting on, a note beside the switch says it “already does this with a setting of its own” and asks you to leave the job to one of them.
Recommended settings
We recommend turning it on for every site. The one reason to wait is a page another site shows inside a frame, such as a booking or donation page embedded on a partner’s site. X-Frame-Options stops that, and the four headers come as one switch.
| Site | What we recommend |
|---|---|
| Agency or many sites | Turn it on from Quick Setup’s Safe fixes as each site is set up, after asking the client whether any page of theirs is shown in a frame elsewhere. |
What it can break, and how to undo
In the finding’s own words: “Could break: almost nothing. If another site legitimately embeds your pages in a frame, that embed would stop working.”
- Framing by another site. Pages shown in a frame on another domain stop showing there. Framing by your own site carries on.
- A file with the wrong type. With
nosniff, a script or stylesheet that WordPress itself sends, such as one a plugin serves through a page address or the REST API, may be refused if its content type is wrong. The .js and .css files your web server serves directly do not carry these headers. - Referrers. Sites you link to see the domain a visitor came from, not the page. Links within your own site keep the full address.
- The Topics API. Ad scripts that rely on it get no topics from your pages.
Undo. Turn the switch off, or run wp bettershield harden security_headers --undo --user=<login>. The headers stop with the next response, and browsers keep nothing from them. Turning it off asks for your password when Ask for my password before removing a protection is on (Settings › General). Safe mode stops the headers while it lasts.
Final Outcome
Findings. Your site doesn’t send some standard browser safety settings (Low, in the Public information about your site area, 3 setup points while open) resolves. It also passes without this fix when your web server was seen sending the headers on a visitor’s page at the daily check.
- The row. “Confirmed on a page a visitor received” with the time. Once the daily check has seen your server send some of the four itself, the line reads, for example, “The headers this plugin sends were on the page a visitor just received, and the web server sends X-Frame-Options itself.”, and those count as sent. If a header is missing and the server was not seen sending it, the line names it and says “Your web server may still be adding it”; check what visitors actually get, as below.
- The activity log. “Hardening applied”, “Hardening undone”, and “Protection checked against a live page” when that check’s answer changes.
- From outside.
curl -sI https://example.com/lists the response headers a visitor gets. All four should be there, once each.
If pages come from a page cache, check a fresh, signed-out page load: a copy cached before the change may not carry the headers yet.
On multisite
Each site turns it on for itself.
Related
This is how you can send the four standard Security headers with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.