How To Keep a Decoy Credential With BetterShield?
Create a deliberately unused application password whose attempted use is refused, recorded, and alerted.
In BetterShield, the switch is under BetterShield › Agents › Agent surface › Decoy credential.
What it does
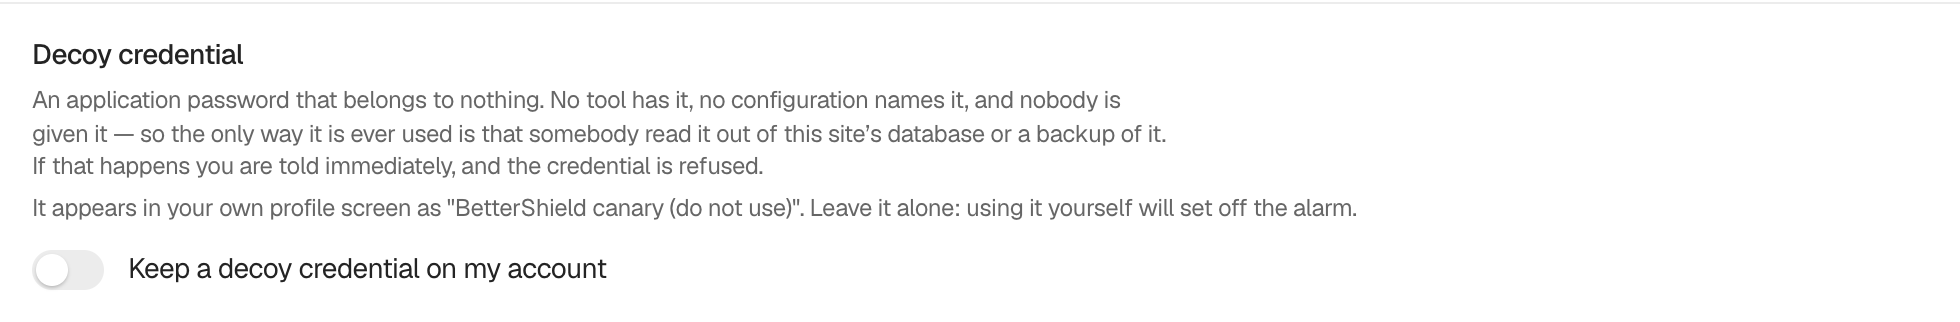
Keep a decoy credential on my account is off by default. It creates an application password named BetterShield canary (do not use). No tool receives the secret and no configuration names it. If the credential is attempted, BetterShield refuses authentication, records the event, and emails an urgent alert even with instant alerts off. Mute all alerts still silences that email.
An attempted use means someone or something obtained the credential value from the database or a backup. It still does not identify who did so.
Step 1: Keep a Decoy Credential
Turn on the switch while signed in as the account that should hold the decoy. Leave the named application password untouched on the WordPress profile screen.
Recommended settings
Use a privileged administrative account whose security alerts are monitored. Never copy or test the decoy secret.
What it can break and how to undo
The decoy cannot authenticate, so assigning it to a real tool makes that tool fail and triggers the alert. Turn the switch off to remove BetterShield’s decoy record and credential.
Final Outcome
The row should state that the decoy is kept and the profile should list BetterShield canary (do not use). Do not test it by using the credential.
On multisite
Application passwords belong to network-wide user accounts. BetterShield records which site planted each decoy.
Related
This is how you can keep a decoy credential with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.