Two-factor and passkeys: setup and role requirements
A tour of BetterShield › Protection › Two-Factor: the summary tiles, your own two-factor and passkeys, and the two requirements you can set by role.
BetterShield › Protection › Two-Factor is where people who manage BetterShield set up their own second factor and decide what the site asks of everyone else. It has your own Two-factor authentication and Passkeys cards side by side, then What the site requires, with Require two-factor of a role and Sign in with a passkey only. Everyone else sets up their own sign-in on their Profile screen, and store customers on My Account › Sign-in security (see Your profile). Everything on this screen is in the free plugin.
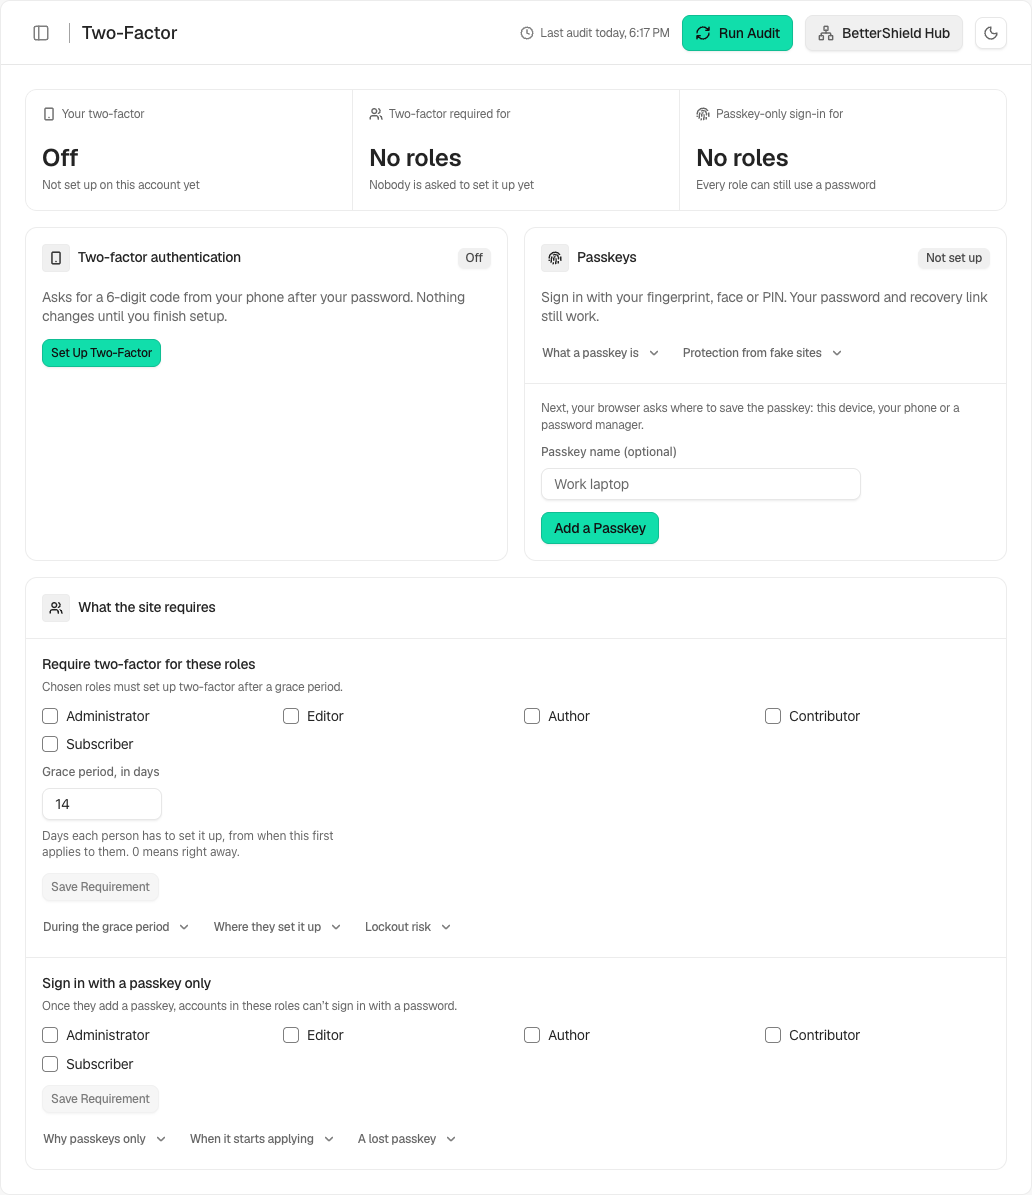
The summary tiles
Three tiles at the top answer the usual questions before you read any card.
| Tile | What it shows | On a new site |
|---|---|---|
| Your two-factor | On with how many backup codes are unused, or Off | Off, “Not set up on this account yet” |
| Two-factor required for | How many roles, and their names | No roles, “Nobody is asked to set it up yet” |
| Passkey-only sign-in for | How many roles, and their names | No roles, “Every role can still use a password” |
Where passkeys cannot work on the site and roles are named, Passkey-only sign-in for reads “Not in effect: passkeys are off on this site”.
Your sign-in
Two-factor authentication sets up a six-digit code from any authenticator app, with ten single-use backup codes, and turns on only at the last step. Once it is on, the card counts your unused backup codes, issues a new set, and turns it off, each after a current code. While safe mode is on, the turn-off takes your password instead, and an alert goes out when it is used. See Two-factor with an app.
Passkeys lets you sign in with your fingerprint, face or device PIN. Name the device, press Add a passkey, prove it is you (a code, your password or a passkey), and confirm on the device. Each account holds up to 10, the site needs HTTPS, and a passkey is an extra way in that leaves your password and codes working. The card lists each passkey with when it was last used. See Passkeys.
What the site requires
Require two-factor of a role asks the roles you tick to set up the app codes. They get a grace period (14 days by default) with a countdown, and after it the dashboard sends them to set it up until they do. Signing in is never blocked by it. A passkey does not count toward it. See Require two-factor.
Sign in with a passkey only stops the password working for accounts in the roles you tick, but only once each account has added a passkey. It needs a working recovery link or printed recovery codes before you can add a role. See Passkey-only sign-in.
Each has its own Save requirement button, and a line beside it says Unsaved changes until you press it.
Members Outside the Dashboard
In BetterShield 1.1.7 or newer, What the site requires also contains Sign-in Security Page. Publish a page with the Sign-in Security block or [bettershield_account] shortcode, then select it under Page. None is the default. See Set up a Sign-in Security page.
On a store, Show Sign-in security on WooCommerce My Account starts on. Turning it off hides the tab only from customers with no applicable requirement, two-factor setup or passkey; people who need to manage existing security still see it.
Recommended settings
Set up two-factor and add a passkey for your own account first. Then require two-factor of Administrator and Editor (plus Shop manager on a store) with the default 14 days. Leave passkey-only off until the people in a role already sign in with passkeys. The feature docs explain why, site by site.
On multisite
On BetterShield › Network, a network administrator can set Require two-factor across the network and Passkey-only roles across the network. Both start as Not set. They are a floor: each site enforces the network’s roles plus its own, and cannot untick a role the network requires. Where both set a grace period, the shorter one applies. Each feature doc has the details, and Multisite networks covers the Network screen.
A person’s two-factor setup belongs to their account, so it applies on every site of the network. Passkeys are shared by the sites that use the network’s own domain; a site on a domain of its own needs its own passkey.