How To Tell Browsers to Use Only HTTPS (HSTS) With BetterShield?
Send the HSTS header with BetterShield: prove it at five minutes, move to six months, choose subdomains, and know what undo cannot reach.
In BetterShield, Strict HTTPS (HSTS) sends the Strict-Transport-Security header, usually called HSTS. A browser that has seen it uses only HTTPS for your site until the time it was given runs out. It is under HTTPS and browser security on BetterShield › Protection › Hardening, and it starts off. Its effect outlives its undo, which is why it starts at five minutes.
What it does
- It “adds Strict-Transport-Security to front-end pages, the sign-in page, the dashboard and the REST API, on HTTPS requests only.”
- If WordPress or another plugin already sets the header, it is left exactly as it is, and so is one your web server adds, once the daily check has seen it.
- It never adds preload: “that is a submission to a list built into browsers, and removal from it takes months.”
- It is not offered unless the site’s address is already HTTPS.
| Choices | Header sent |
|---|---|
| Five minutes, this domain only | max-age=300 |
| Six months, this domain only | max-age=15768000 |
| Either, with every subdomain | the same, plus ; includeSubDomains |
Each HTTPS page a browser loads starts the period again.
Step 1: Open Not available here
Check that the site address is https://. If not, the row reads Not available here with the reason.
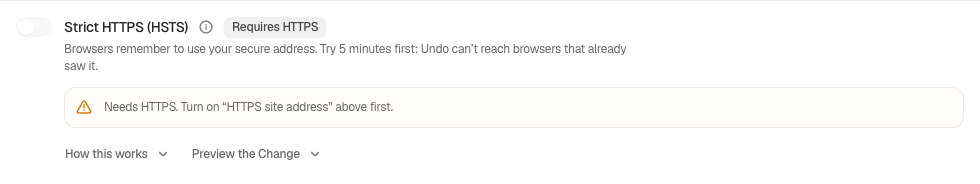
Step 2: Tell browsers to use only HTTPS (HSTS)
- Find Strict HTTPS (HSTS) under HTTPS and browser security.
- Keep the preselected choices and press Preview the change. Its first line ends with the exact header,
max-age=300. - Turn the switch on. The row shows On since, the header value with Copy, and Undo never expires.
- After a few days of ordinary use, move to six months: turn the switch off, choose Six months, once you have lived with the short one, and turn it on again. The choices only show while the switch is off.
| Option | What it does | Default |
|---|---|---|
| How long browsers should insist | Five minutes, to prove it works or Six months, once you have lived with the short one. | Five minutes |
| Include subdomains | This domain only, or Every subdomain as well: every host name under the site’s own. | This domain only |
Monitor first has no watch mode here; the five-minute setting is the trial. From the terminal, wp bettershield harden hsts --user=<login> applies five minutes on this domain only; add --mode=long for six months or --subdomains=yes for every subdomain. See WP-CLI commands.
A connected AI assistant may apply the five-minute, this-domain-only form on its own. Six months, or every subdomain, needs your agreement first.
Recommended settings
We recommend it for any site fully on HTTPS with a certificate that renews on its own: five minutes through ordinary use (pages, forms, signing in, the dashboard), then six months. Keep This domain only unless you know every subdomain answers on HTTPS. Leave it off while a move to HTTPS is still in progress.
| Site | What we recommend |
|---|---|
| Store (WooCommerce) | Place a test order from cart to confirmation during the five-minute period. |
| Agency or many sites | Keep This domain only on client sites whose DNS you do not manage: you cannot see which subdomains exist. |
What it can break, and how to undo
- A lapsed certificate. Browsers that saw the header cannot fall back. If the certificate expires within 21 days, a note beside the switch asks you to renew it before applying.
- A subdomain on plain HTTP. With Every subdomain as well, it stops opening in browsers that saw the header. The field calls this “the part that most often takes something unrelated offline.”
- HTTPS that ends at a proxy. If a proxy, load balancer or CDN handles the encryption without telling WordPress, the header is never sent, and the row says “applying this changes nothing” until wp-config.php sets the HTTPS server variable. See Server compatibility.
- A header your server adds. Once a day BetterShield asks the site’s own front page whether your web server sends HSTS itself, and once it has seen one, it leaves the header to the server rather than sending a second.
Undo. Turning the switch off, or --undo, stops the header at once. It cannot reach browsers that already saw it: they keep insisting on HTTPS for five minutes after their last visit, or six months at the long setting. Undo never expires is about the switch, not those browsers. To step down from six months, switch to five minutes (and This domain only) and leave it on: a browser that comes back over HTTPS replaces its stored rule.
Turning it off asks for your password when Ask for my password before removing a protection is on (Settings › General). Safe mode stops the header while it lasts.
Final Outcome
The row. “Confirmed on a page a visitor received”, with the time. Behind a proxy that hides HTTPS, it says the last page “reached WordPress over plain HTTP, so this header could not be seen on it.”
- The activity log. “Hardening applied”, “Hardening undone”, and “Protection checked against a live page” when that check’s answer changes.
- Findings. No finding opens while it is off. While it is on, Some protections that are switched on are not working (Medium) names it if a visitor’s page was seen without the header. The site address is not HTTPS (Critical on a live site) means it cannot be offered yet; The site’s certificate is close to expiring (Medium, rising to Critical) means renew first.
- From outside.
curl -sI https://example.com/ | grep -i strict-transportprints what visitors get.
On multisite
Each site turns it on for itself. On the main site of a subdomain network, Every subdomain as well means every site, and all of them must already be on HTTPS. On a subdirectory network every site shares one host name, so a header from any of them covers them all.
Related
- Hardening
- Security response headers
- Content security policy
- Server compatibility
- HSTS in WordPress, explained
This is how you can tell browsers to use only HTTPS (HSTS) with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.