How To Rotate WordPress Sign-in Keys With BetterShield?
Mix a strong secret into the keys that sign every WordPress session, rotate them after a suspected compromise, and know who gets signed out.
With BetterShield, mix a strong secret into the keys that sign every WordPress session, rotate them after a suspected compromise, and know who gets signed out.
What it does
WordPress signs every sign-in session with the keys and salts in wp-config.php. Sign everyone out on demand mixes a strong secret of BetterShield’s own into every key WordPress derives, so forging a session needs both, and adds Rotate keys now for after a suspected compromise. Applying, rotating and undoing all sign every other session out, your own other devices included. It is under Signing in on BetterShield › Protection › Login & Access, and it starts off. On a multisite network it is done from the Network screen instead (see below).
- Generates a strong secret and mixes it into every key WordPress derives, using the mechanism WordPress provides for exactly this. The secret is never shown.
- Does not edit wp-config.php. The keys in force become a combination of both, so someone holding a copy of wp-config.php alone cannot forge a session.
- Signs every other session out the moment it is applied. Made from the dashboard, the browser you are using stays signed in and your other devices are signed out. Made from WP-CLI or by an AI assistant, every session ends, yours included.
- Changes no password. Everybody signs back in with the password they already have. Application passwords are not sessions, so tools using them carry on.
- Adds a rotation. Rotate keys now replaces the secret and signs everyone out the same way again.
The secret stays in use during safe mode, so starting or ending safe mode signs nobody out.
Step 1: Open BetterShield › Protection › Login & Access
Open BetterShield › Protection › Login & Access and find Sign everyone out on demand under Signing in. The note beside the switch says whose sessions will end.
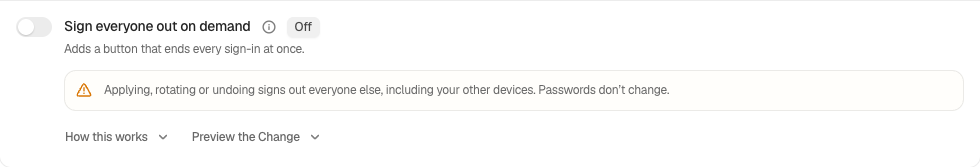
Step 2: Strengthen and rotate the WordPress sign-in keys
- Pick a quiet time: everyone signed in will have to sign in again.
- Press Preview the change. Nothing changes.
- Turn the switch on. The row reads On since and Undo never expires, with the note “Every other session was signed out; yours was kept.”
It has no options. Monitor first cannot measure this fix: its panel says to rely on the preview, a staging copy and undo instead.
Before it applies
Like every Signing in fix, applying it first checks your way back in: a working recovery link or unused recovery code, checked within the last day. If that fails, Check the way back in first offers Check now (or Open Recovery) and Go ahead anyway, which is logged. See Set up recovery. Applying needs a signed-in browser, not an application password.
Rotate keys now
Once the fix is on, the row has Rotate keys now.
- Press Rotate keys now. The row restates what will happen: “Generates a new secret. Every other session is signed out; yours is kept. Do this after a suspected compromise, or on a schedule you choose.”
- Press Yes: Rotate keys now, or Cancel.
- The row then reads “Keys last rotated” with the date and time, and “Every other session was signed out; yours was kept.”
A rotation has no undo: the previous secret is not kept anywhere. It needs a signed-in browser, and your password if Ask for my password before removing a protection is on.
From WP-CLI
wp bettershield harden auth_keys --dry-run
wp bettershield harden auth_keys --user=admin
From the terminal there is no session to carry over, so applying signs every session out, yours included. Rotate keys now has no WP-CLI command. See WP-CLI commands.
Recommended settings
We recommend applying it on every single site, at a quiet hour, and rotating after a suspected compromise, after someone who had access to the server or database leaves, or on a schedule you choose. Rotating ends sessions, not passwords, so after a suspected compromise also change the password of any account you think was used.
| Site | What we recommend |
|---|---|
| Store (WooCommerce) | Apply and rotate at your quietest hour: signed-in customers are signed out too. |
| Membership or course site | The same: every member is signed out. If you rotate on a schedule, tell members when. |
| Agency or many sites | Rotate on each client site when someone with server access leaves your team. |
What it can break, and how to undo
- Everyone else is signed out, store customers and members included. Nothing is lost; they sign in again.
- A page cache. When the site uses one, the note beside the switch says a page cache may keep serving cached pages to signed-out visitors until it clears.
- Your other tabs. Reload any dashboard tab you had open before saving in it.
- Deactivating BetterShield while the fix is on stops the secret being mixed in, which signs everybody else out. Done from the Plugins screen, your own session is kept, and BetterShield’s row there says so first: “Deactivating it signs everybody else out: the sign-in key it rotated stops applying. Your own session is kept.” Reactivating works the same way round. From WP-CLI there is no session to keep. Undo the fix first if you would rather nobody was signed out.
To undo, turn the switch off. The keys go back to what wp-config.php alone gives, which is a change of key too: every other session is signed out again, and yours is kept. Undo needs a signed-in browser, and your password if Ask for my password before removing a protection is on. From the terminal, wp bettershield harden auth_keys --undo --user=admin signs every session out, yours included.
What undo cannot reach: sessions that were ended stay ended, and a rotation cannot be put back.
Final Outcome
The row. On since, the last note, and “This one has no effect a page view can check, so it is reported from your settings.”
- Another browser. One that was signed in before you applied or rotated is now signed out.
- The activity log. Applying is “Hardening applied”, rotating is “Authentication keys rotated”, and undoing is “Hardening undone”. Each is followed by “Sessions signed out” (Medium).
- Findings. This fix does not change wp-config.php, so it never clears Your site’s security keys are missing or weak (High). That finding asks you to replace the eight lines in wp-config.php with a fresh set from the WordPress.org secret-key generator. Both are worth doing, and neither does the other’s job. While the fix is on, Some protections that are switched on are not working (Medium) names it if it reads as on but is no longer in force, for example because another plugin took it off.
On multisite
One sign-in covers every site of a network, so the keys are shared. On a site’s own screen the row reads Not available here and says why. A network administrator rotates them from the Network screen in Network Admin: tick I understand every other session on every site will end, then press Rotate the sign-in keys. Every session on every site ends except yours, and it cannot be put back. See Multisite networks.
Related
This is how you can rotate WordPress sign-in keys with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.