How To Retire Unused Application Passwords With BetterShield?
Run a daily sweep that revokes application passwords after a chosen period without use.
In BetterShield, the retirement control is under BetterShield › Agents › Agent surface › Retire unused application passwords.
What it does
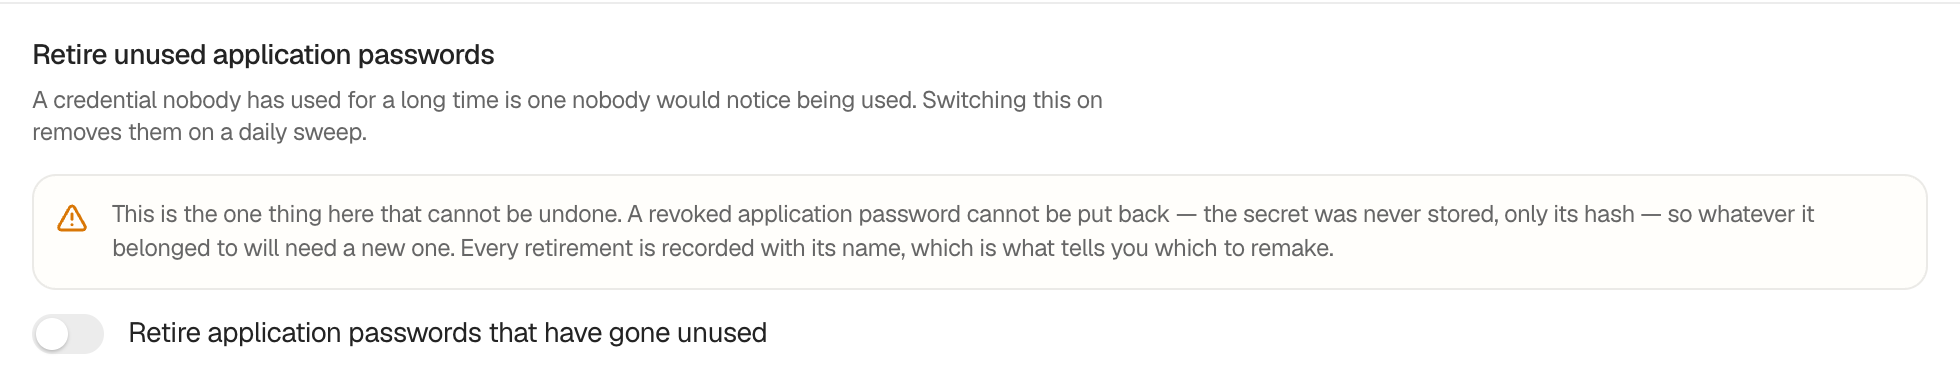
Delete unused application passwords is off by default. When enabled, a daily sweep revokes credentials after Unused for (days), which defaults to 180 and has a minimum of 30. It skips the credential currently authenticating the sweep and BetterShield’s decoy credential. Each retirement is recorded with the credential name.
Step 1: Retire Unused Application Passwords
Turn on the switch, set the unused period, and save. Review the Application passwords list first for credentials used by infrequent scheduled work.
Recommended settings
Use 180 days unless you know every connected tool runs more often. Choose a period longer than quarterly jobs need.
What it can break and how to undo
Revocation cannot be undone because WordPress stores only the credential hash. A connected tool will stop authenticating and needs a new application password. Turning the switch off prevents future retirement but does not restore credentials already revoked.
Final Outcome
Confirm the setting stays on and the chosen day count is shown. Review Activity for retirement records after a sweep runs.
Related
This is how you can retire unused application passwords with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.