How To Protect Private Files With BetterShield?
Answer requests for wp-config backups, logs, database dumps, .git and .env with a 404, using .htaccess rules on Apache or LiteSpeed's paid edition.
With BetterShield, answer requests for wp-config backups, logs, database dumps, .git and .env with a 404, using .htaccess rules on Apache or LiteSpeed’s paid edition.
What it does
In BetterShield, some files say too much when fetched by address: a wp-config.php backup served as text, a debug log, a database dump, an exposed .git folder. Private file protection answers requests for them with a 404, through .htaccess, so it needs Apache, or LiteSpeed’s paid edition. It is off until you turn it on, under Hide site details on BetterShield › Protection › Hardening.
It writes one marked block at the end of your site’s .htaccess (the file WordPress keeps its permalink rules in), from # BEGIN BetterShield sensitive-files to # END BetterShield sensitive-files, and touches nothing outside it. Where the server reads .htaccess, requests for these answer 404, in any folder:
| What | For example |
|---|---|
| Copies and backups of wp-config.php: wp-config.php with anything after it, wp-config followed by a dot, dash or underscore, and wp-config names ending in a backup or archive extension (only at the top of the WordPress folder or the site’s home folder) | wp-config.php.bak, wp-config.php~, wp-config.old, wp-config.zip |
| Log files | debug.log, anything ending .log, error_log |
| Database dumps | files ending .sql, or .sql packed as .gz, .zip, .bz2, .xz, .7z, .tgz, .tar, .tar.gz or .rar |
| Editor swap files | .swp, .swo and similar |
| Files every WordPress install ships | readme.html, license.txt, wp-config-sample.php |
| Version control and environment files | .git, .svn, .hg, .env |
| Server files | .htaccess and .htpasswd, and copies of them |
- 404, not 403, whether or not the file exists, so a refusal does not confirm it is there.
- wp-config.php itself is not on the list. Requested from a browser, it runs and shows nothing.
- It hides files; it does not delete them.
Step 1: Open BetterShield › Protection › Hardening
Open BetterShield › Protection › Hardening and find Private file protection under Hide site details.
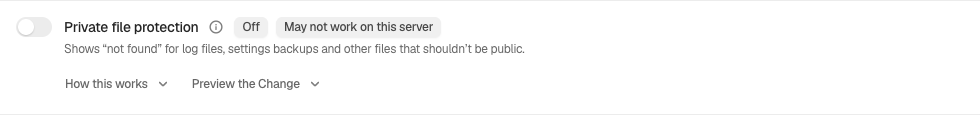
Step 2: Protect Private Files
- Press Preview the change. It lists what applying would do and changes nothing.
- Turn the switch on. The row shows On since and Undo never expires.
It has no options, and Monitor first cannot watch it in advance: its panel points you back to the preview. From WP-CLI, wp bettershield harden sensitive_files --user=admin applies it and adding --undo reverses it. An AI assistant cannot apply or remove it: it writes to .htaccess, so it stays your own switch.
What the row can say before you apply it:
| Your site | What the row shows |
|---|---|
| On nginx or IIS | Not available here: the server “does not read .htaccess files, so this fix cannot work here. The same rules can be set in the server configuration; your host can add them.” |
| On LiteSpeed | Available, with a note that LiteSpeed’s paid edition reads these rules and the free OpenLiteSpeed skips them, so whether they are enforced could not be confirmed |
| On OpenLiteSpeed | Not available here: it “reads only rewrite rules from .htaccess files and skips the kind this fix writes”; your host can set the same protection in the server configuration |
| On a server BetterShield does not recognize | Available, with a note that the rules will be written but BetterShield could not confirm they are enforced |
| Another plugin has rules in .htaccess | A note naming it. This block never touches theirs; if both refuse the same request, the earlier rule answers. |
| A site on a network other than the main site | Not available here (see below) |
Applying is refused, with nothing written, when .htaccess is not writable, or when the site address and WordPress address point somewhere other than where the files are. See Server compatibility.
Recommended settings
Turn it on for any site on Apache, or LiteSpeed’s paid edition, then delete any such file you do not need: hidden is good, gone is better. On nginx, IIS or OpenLiteSpeed, ask your host for equivalent rules in the server configuration. On a network, apply it once, from the main site.
What it can break, and how to undo
- Files you publish on purpose with these names. A .log or .sql file meant for download, or a readme.html you link to, answers 404 too. Rename it.
- Tools that read readme.html or license.txt. They stop getting them, which is the point.
- A server that refuses the rules. If pages stop loading right after you apply it, your host likely does not allow these rules in .htaccess. Run
wp bettershield harden sensitive_files --undo --user=admin, or delete the block over SFTP or your host’s file manager and then turn the switch off.
To undo, turn the switch off. It removes exactly its block; if BetterShield created .htaccess and nothing else was added, the file goes too. With Ask for my password before removing a protection on, undo asks for your password.
If anyone edited inside the block, undo leaves it alone and the row says the last undo did not complete. Keep whatever was added, delete the block by hand, then turn the switch off again.
The block stays in .htaccess, and keeps working, while safe mode is on and while BetterShield is deactivated. Deleting BetterShield keeps it too, unless you chose to remove its records under When this plugin is deleted on Settings › General.
Final Outcome
From outside. In a private window, open /readme.html and /license.txt. You get a 404 instead of the file.
- The row. “This one has no effect a page view can check, so it is reported from your settings.” Hence the outside check.
- The activity log. “Hardening applied”, or “Hardening could not be applied” if it was refused.
- Findings. Files that should be private can be downloaded from this site (Critical) comes from a weekly check that asks your site for a few such files (wp-config backups, .env, .git/config, debug.log, common database dump names) and reports only what really came back. With the rules working those requests get 404, so the finding clears after the next weekly check. The files are still there: in the finding’s words, removing one “is yours to do, and it is worth keeping a copy somewhere outside the web root first.”
Good to know
It does not cover leftover tools such as an installer script or a database manager. Those are reported separately, as A leftover setup or database tool is publicly reachable.
On multisite
Every site on a network shares one .htaccess. In the row’s words: “Apply this from the network’s main site; it protects all of them.” On any other site it reads Not available here.
Related
- Hardening
- Stop PHP in uploads
- Stop uploads listings
- Hide the WordPress version
- Server compatibility
- Score and findings
This is how you can protect private files with BetterShield.
Getting Stuck? Feel free to contact our Dedicated Support Team.